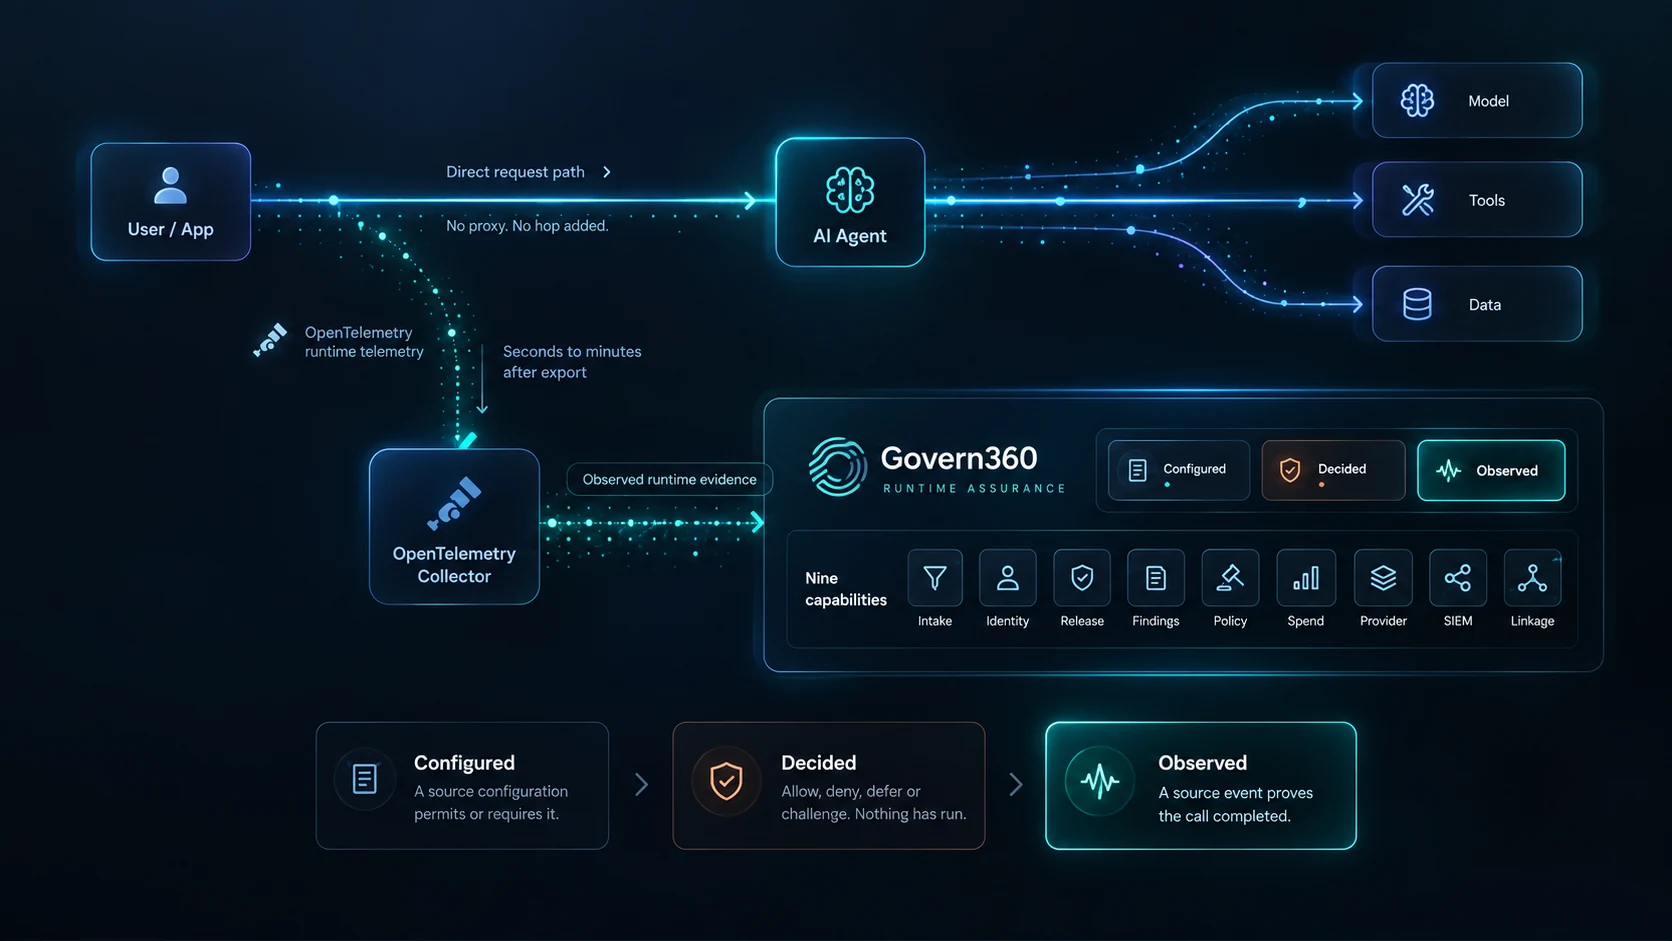
Does Govern360 sit inline in the request path?
No. Runtime evidence reaches Govern360 because the customer’s own OpenTelemetry collector exports traces to it. Govern360 receives those traces; it is not a hop the request passes through, adds no latency, and cannot hard-stop a call at request time. Every product that sees runtime by sitting in the path is a proxy you have to defend a latency budget for. This one is not.
What does Govern360 mean by real-time?
Seconds to minutes after the source exports. It never means inline blocking. The figure depends on the customer’s collector export interval, not on anything Govern360 controls, so the honest description is that evidence lands shortly after the span is exported rather than at the moment of the call.
Configured means a source configuration permits or requires it — read from the agent’s setup, which it may never have exercised. Observed means a source event proves the call completed. Govern360 reports both, and never merges them: a policy decision such as a DENY is a permission or a refusal, not an observed action, and is never drawn as one.
How does runtime telemetry reach Govern360?
Traces arrive in standard OpenTelemetry format from the collector the customer already runs. Each connector holds its own token with an expiry, rotation with overlap and a quota, and at most two live tokens at a time. Test connectors are kept separate from production so trial traffic never lands in production evidence.
How is a trace matched to a known agent?
Only by an exact identifier. A name that merely looks like a match is not accepted — it goes to a review queue for a person to confirm. Guessing here would attach real runtime behaviour to the wrong agent, which is worse than leaving it unattributed.
What is Release Certification?
A tiered, signed approval for a production agent, tied to its model, purpose, tools and autonomy tier. If any of those pinned parts change, the approval is marked changed rather than silently remaining valid, and it expires on a schedule. An approval is a statement about a moment; agents change weekly, so the certificate has to know when it has been outrun.
What do runtime findings actually catch?
Agents that were retired but are still running, agents in production with no current certificate, model drift away from what was approved, tools being called that are not on the approved list, and data going to destinations outside the allow list. They are checked hourly and raised into the existing alert feed rather than a second parallel pipeline.
Does a runtime finding block or stop an agent?
No. A finding is evidence, not enforcement. It never blocks, never stops an agent and never changes a certificate. Where an enabled policy blocks a tool and the source reports the call completed anyway, the finding says the block did not hold — and it says that only when the source actually reported completion, never on suspicion.
Can we test a policy without enforcing it?
Yes. A dry run asks the live decision engine what it would decide, with nothing enforced. A dry run is never a decision: it reads not enforced, never enters the decision log, and never opens an approval request. You can also replay the last 30 days of observed tool calls against today’s rules to see what a proposed change would have done.
How does runtime evidence change what we are billed?
By itself, not at all. Each model call is marked as confirmed by both sources, seen only at runtime, or seen only in spend records. The interesting column is the middle one — it ran, and it is in nobody’s bill. Counting runtime-only usage is opt-in per organisation and counts from the moment it is switched on, so no closed month ever moves.
What is provider posture?
A single read, per AI provider, putting the connection, keys, projects, admin log, spend and runtime activity side by side. It writes nothing, calls no provider and reads no credential. Gaps are named in words: a provider with no connection reads not visible, never no keys; an admin log that could not be read says so with the reason.
Can runtime findings go to our SIEM?
Yes, outbound only and off by default, through the existing SIEM forwarding rather than a new channel. For auditors there is a runtime assurance evidence pack with a SHA-256 checksum list, so what you hand over can be shown not to have changed since it was generated.
Does runtime telemetry mean you now store our prompts?
No. The capture mode permits metadata only and nothing else is accepted. Prompt text and model responses are never stored. What arrives is span metadata — which model, which tool, which destination, how many tokens — not what anyone typed.
Can you see which employee triggered an agent?
Not by name on default screens. The initiator is stored as an HMAC under a per-organisation key held inside the database, together with the type of initiator. Runtime findings are about agents, not scores of people.
What do the runtime screens show before we connect telemetry?
They say no runtime telemetry is connected. They never show zero runs, because zero is a measurement and this is an absence of one. If a connector exists but nothing arrived in the window, it says no events were observed in connected telemetry during the selected period — which is a different statement, and the difference matters.
What does Govern360 see at runtime?
What the agent actually did — from traces exported by the customer’s own telemetry collector, without sitting in the request path. That covers runtime intake, agent identity resolution, release certification, runtime findings, policy dry runs and replay, runtime spend reconciliation, provider posture, SIEM forwarding with an evidence pack, and linkage maps on every runtime surface.